2026 Edition
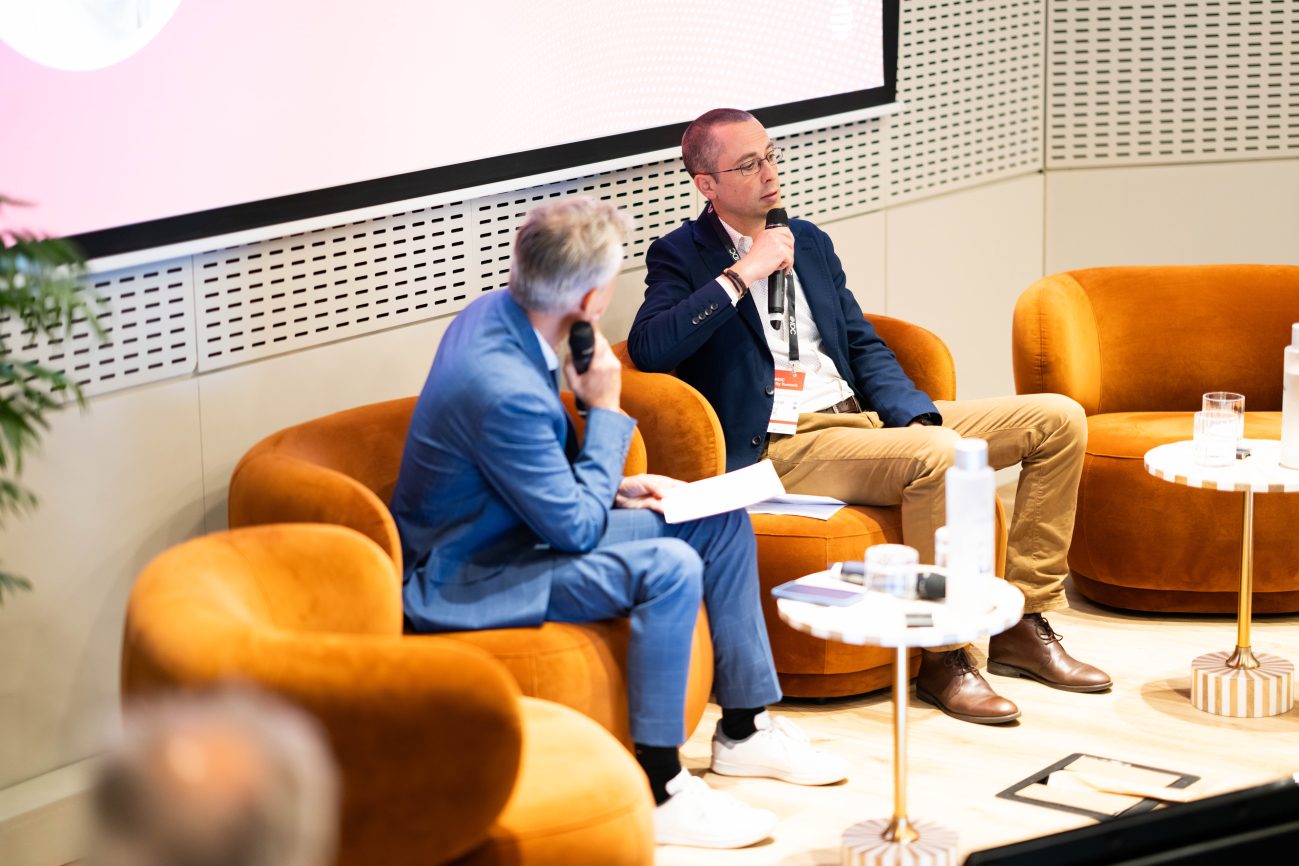
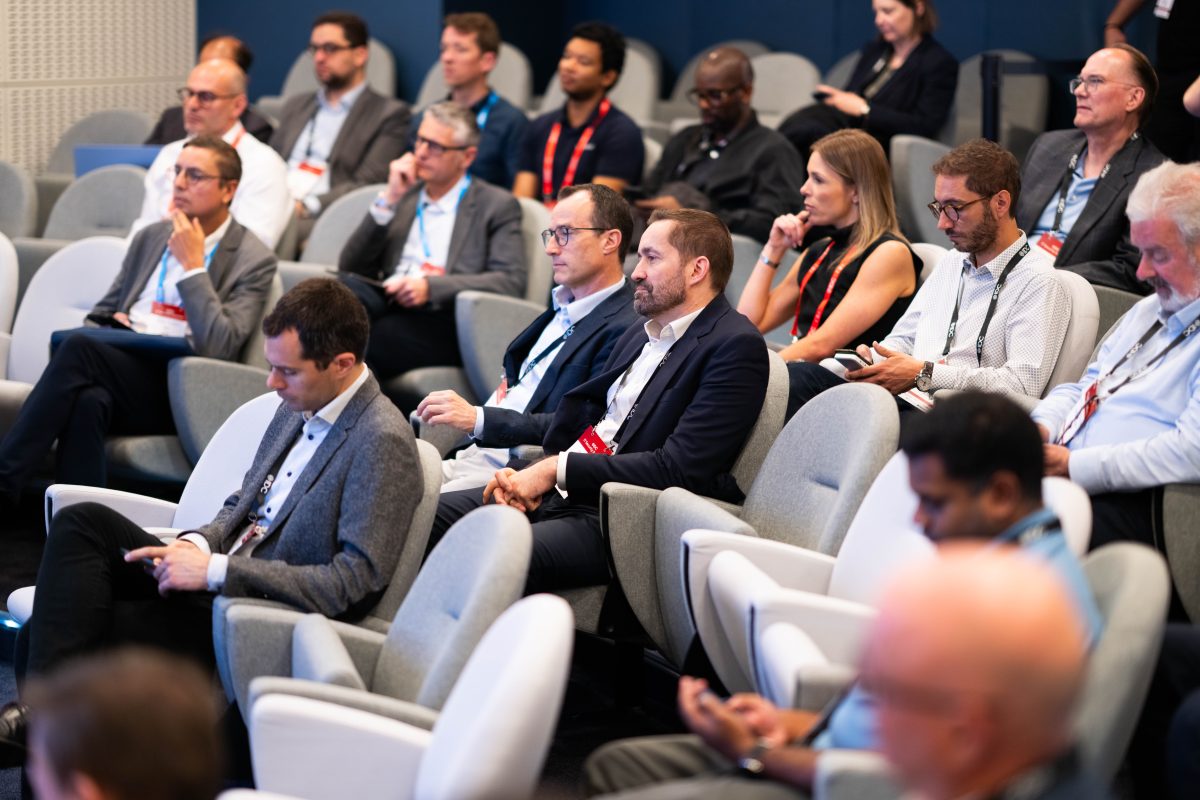
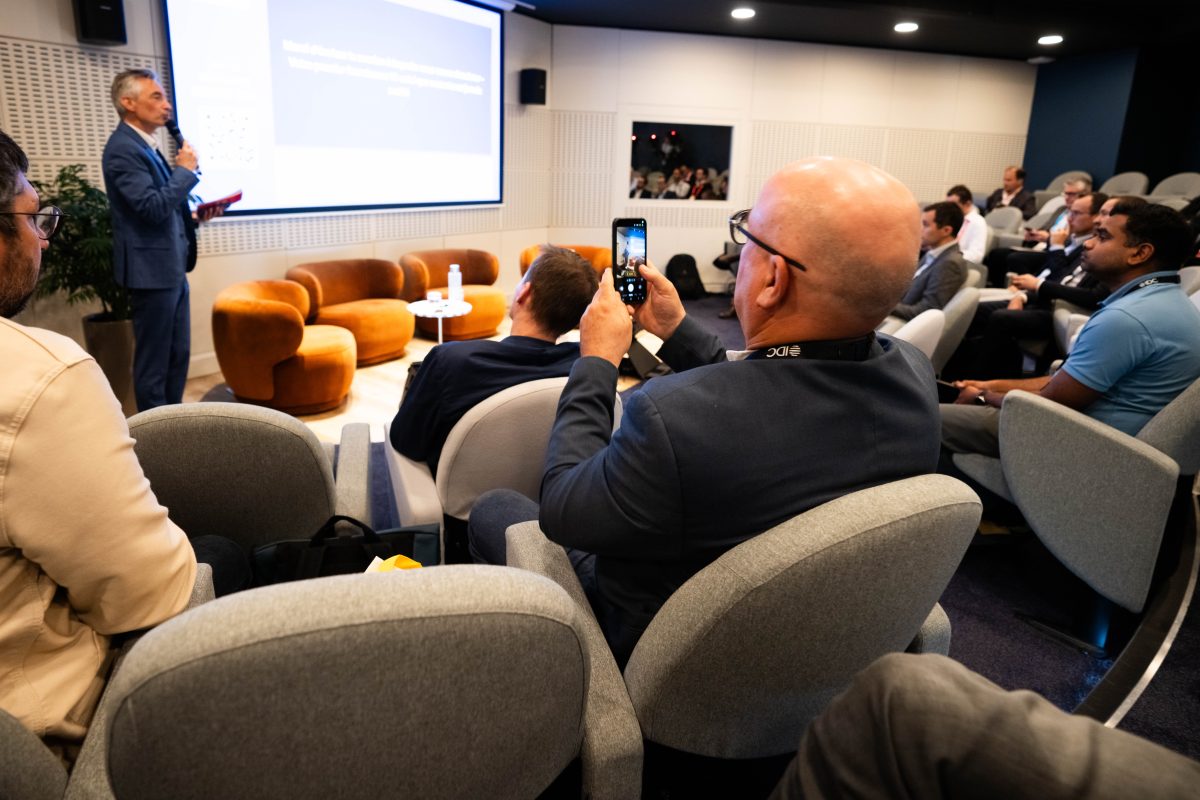
The IDC IT Security Summit France 2026 brought together cybersecurity decision-makers to discuss emerging threats, organizational resilience, and the impact of AI and geopolitics on security strategies.
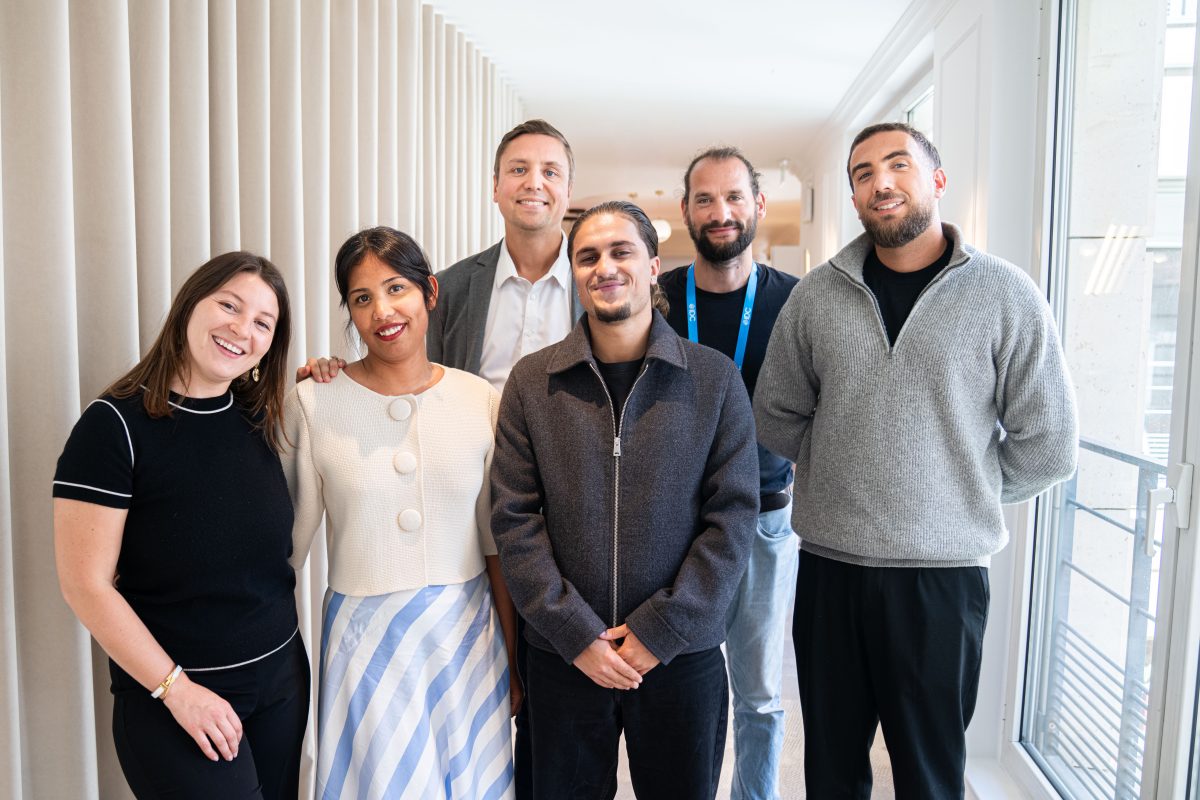
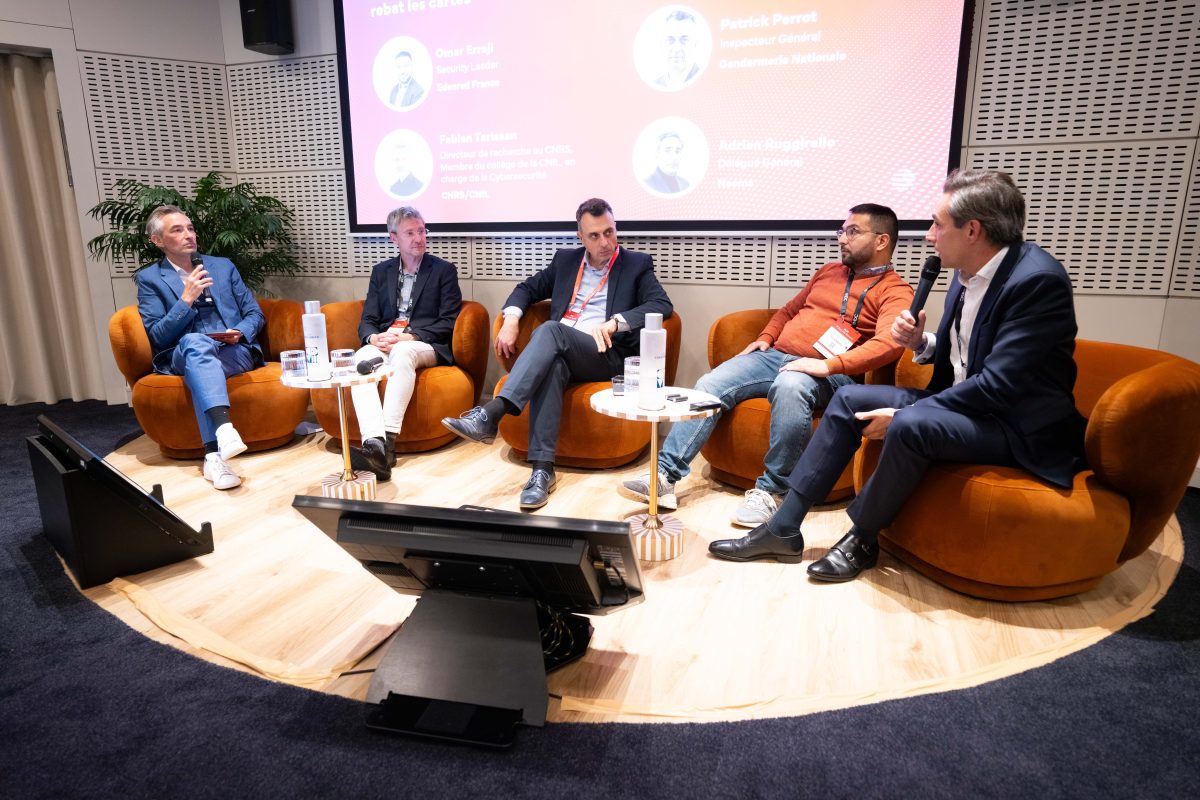
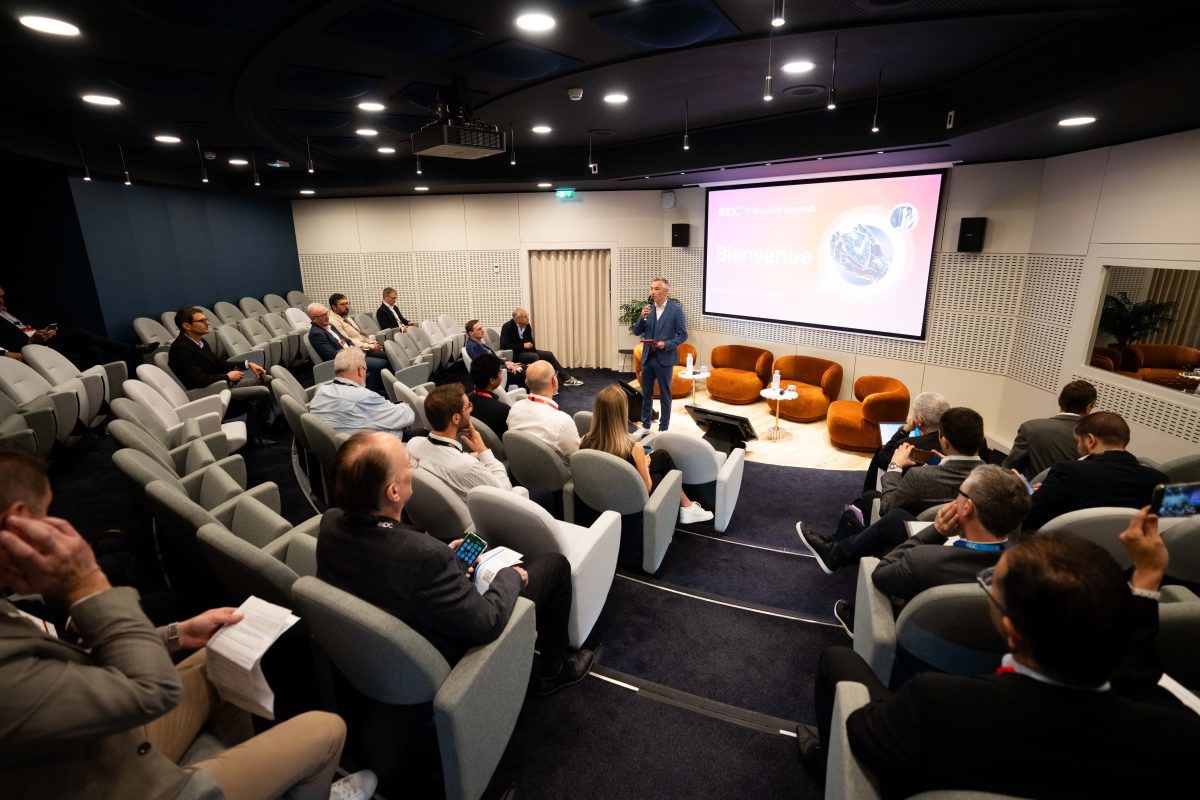
Photo Gallery
Speakers
Thibaut Roynette
RSSI France
DANONE
Read Bio
Pierre Kochanski
Directeur Coordination des Technologies de l’Information
MINISTERE ECONOMIES ET FINANCES
Read Bio
Othmane Erraji
Security Leader
EDENRED FRANCE
Read Bio
Emilie Brié-Philippe
RSSI, Caisse des Dépôts – Direction des Politiques Sociales Conseillère du Commerce Extérieur
Vice-Présidente du Groupe d'Intelligence Économique
Read Bio
Reynald Hazard
Cybersecurity General Manager
FRAMATOME
Read Bio
Vincent Gapaillard
RSSI Groupe
LOXAM
Read Bio
Eugénie Laurian
Experte I Stratégie en sécurité numérique: cybersécurité et protection des données
MINISTERE DES ARMEES
Read Bio
José Araujo
Directeur de la Cybersecurité
SNCF/e.solutions SNCF
Read Bio
Patrick Perrot
Inspecteur Général
INSPECTION GENERALE GENDARMERIE NATIONALE
Read Bio
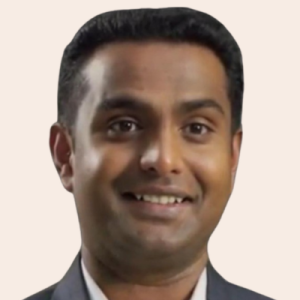
Suvansh Lal
CISO
EQUANS FRANCE
Read Bio
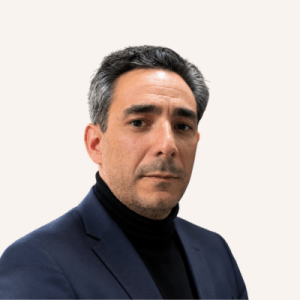
Adrien Ruggirello
Délégué Général
NEOMA
Read Bio
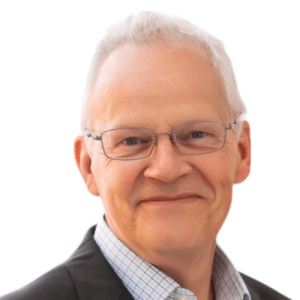
Duncan Brown
Group Vice President, IDC Europe
IDC
Read Bio
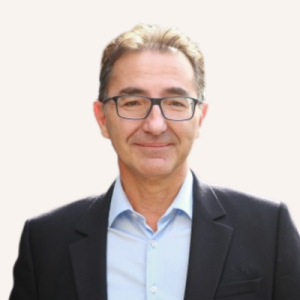
Bruno Durand
VP Sales Southern Europe
Sophos
Read Bio
Uriel Marie-Sainte
Enterprise Solutions Engineer – EMEA
1Password
Read Bio
Amine Beyaoui
Read Bio
Thomas Gricar
Senior Regional Account Manager
Horizon3.ai
Read Bio
Alexandre Lamy
Sales Leader
Chainguard
Read Bio
Guillaume Rameaux
Modérateur
IDC
Read Bio
Thibaut Roynette
Event Sessions
One Day Event 9:35 am
Panel #1 – Digital Sovereignty vs Economic Reality: An Unsolvable Dilemma?
Cross-perspectives on strategic trade-offs between digital sovereignty and economic constraints.
Thibaut Roynette, CISO, Danone
- Trade-offs between sovereignty and economic performance
- Technological dependencies and strategic choices
- Pathways toward realistic autonomy
Pierre Kochanski, CISO, Ministry of Economy and Finance
- Geopolitical and regulatory constraints
- Tensions between competitiveness and security
- Regulatory framework and national sovereignty
Suvansh Lal, CISO, Equans France
- Economic reality of large corporations
- Impact of dependencies on strategic decision-making
- Concrete steps toward greater autonomy
Pierre Kochanski
Event Sessions
One Day Event 9:35 am
Panel #1 – Digital Sovereignty vs Economic Reality: An Unsolvable Dilemma?
Cross-perspectives on strategic trade-offs between digital sovereignty and economic constraints.
Thibaut Roynette, CISO, Danone
- Trade-offs between sovereignty and economic performance
- Technological dependencies and strategic choices
- Pathways toward realistic autonomy
Pierre Kochanski, CISO, Ministry of Economy and Finance
- Geopolitical and regulatory constraints
- Tensions between competitiveness and security
- Regulatory framework and national sovereignty
Suvansh Lal, CISO, Equans France
- Economic reality of large corporations
- Impact of dependencies on strategic decision-making
- Concrete steps toward greater autonomy
Othmane Erraji
Event Sessions
One Day Event 2:55 pm
Panel #2: Cybersecurity Operating Models in the Age of AI
Expert and executive perspectives on:
- the decline of centralized security models and the structures taking their place,
- how organizations can keep pace with AI-driven threats that outrun human response,
- the shifting roles of CISOs, teams, and leadership in an AI-first security landscape.
Emilie Brié-Philippe
Event Sessions
One Day Event 2:10 pm
CISO and Digital Sovereignty in the Public Sector: From Technical Constraints to Strategic Autonomy
A firsthand look at the CISO’s growing influence in the digital sovereignty debate — from managing technological dependencies to repositioning the security function as a true strategic partner to executive leadership.
Reynald Hazard
Event Sessions
One Day Event 12:40 pm
Supply Chain Attacks: Tackling Third-Party Risk Inside Large Organizations
An interview on the real-world impact of supply chain attacks and how security leaders navigate the organisational fallout.
José Araujo, Director of Cybersecurity, Groupe SNCF
- How ecosystems amplify third-party risk exposure
- Operational chaos and crisis response in practice
- Hard-won lessons and concrete actions to strengthen your supply chain security
Reynald Hazard, Cybersecurité General Manager, Framatome
- Critical supply chain: when a vendor breach triggers physical impact
- Third-party risk in industrial environments: auditing and monitoring without compromise
- From vulnerability to resilience: concrete methods and actionable takeaways
Vincent Gapaillard
Event Sessions
One Day Event 11:55 am
Managing a Cyber Crisis: When the Board Enters the War Room
A firsthand account of cyber crisis management, from the war room to the boardroom.
Vincent Gapaillard, CISO, Loxam
- The CISO’s role in a crisis situation
- Interactions with the board under pressure
- Decision-making dynamics in the war room
- Key lessons drawn from his experience
Eugénie Laurian
Event Sessions
One Day Event 2:10 pm
CISO and Digital Sovereignty in the Public Sector: From Technical Constraints to Strategic Autonomy
A firsthand look at the CISO’s growing influence in the digital sovereignty debate — from managing technological dependencies to repositioning the security function as a true strategic partner to executive leadership.
José Araujo
Event Sessions
One Day Event 12:40 pm
Supply Chain Attacks: Tackling Third-Party Risk Inside Large Organizations
An interview on the real-world impact of supply chain attacks and how security leaders navigate the organisational fallout.
José Araujo, Director of Cybersecurity, Groupe SNCF
- How ecosystems amplify third-party risk exposure
- Operational chaos and crisis response in practice
- Hard-won lessons and concrete actions to strengthen your supply chain security
Reynald Hazard, Cybersecurité General Manager, Framatome
- Critical supply chain: when a vendor breach triggers physical impact
- Third-party risk in industrial environments: auditing and monitoring without compromise
- From vulnerability to resilience: concrete methods and actionable takeaways
Patrick Perrot
Event Sessions
One Day Event 2:55 pm
Panel #2: Cybersecurity Operating Models in the Age of AI
Expert and executive perspectives on:
- the decline of centralized security models and the structures taking their place,
- how organizations can keep pace with AI-driven threats that outrun human response,
- the shifting roles of CISOs, teams, and leadership in an AI-first security landscape.
Suvansh Lal
Event Sessions
One Day Event 9:35 am
Panel #1 – Digital Sovereignty vs Economic Reality: An Unsolvable Dilemma?
Cross-perspectives on strategic trade-offs between digital sovereignty and economic constraints.
Thibaut Roynette, CISO, Danone
- Trade-offs between sovereignty and economic performance
- Technological dependencies and strategic choices
- Pathways toward realistic autonomy
Pierre Kochanski, CISO, Ministry of Economy and Finance
- Geopolitical and regulatory constraints
- Tensions between competitiveness and security
- Regulatory framework and national sovereignty
Suvansh Lal, CISO, Equans France
- Economic reality of large corporations
- Impact of dependencies on strategic decision-making
- Concrete steps toward greater autonomy
Adrien Ruggirello
Event Sessions
One Day Event 2:55 pm
Panel #2: Cybersecurity Operating Models in the Age of AI
Expert and executive perspectives on:
- the decline of centralized security models and the structures taking their place,
- how organizations can keep pace with AI-driven threats that outrun human response,
- the shifting roles of CISOs, teams, and leadership in an AI-first security landscape.
Duncan Brown
Duncan Brown is associate vice president, European Security Practice, at IDC EMEA and leads the firm’s security research program in Europe. He specializes in providing strategic advice to his clients, informing and validating their corporate, product, and marketing plans. Brown is an expert in analyzing the security market globally, and his list of security-related clients includes enterprises, central banks, government organizations, and security product suppliers and services providers. Brown’s expertise spans the gamut of security topics including incident response, threat intelligence, and global privacy issues. He established and leads IDC’s coverage of the global impact of the GDPR, the RPEC (ePrivacy Directive update) and NIS Directive on technology companies and their customers. His analysis and opinions are widely sought by industry leaders and investors, while his comments on industry trends and developments frequently appear in the leading business and trade publications.
Event Sessions
One Day Event 9:00 am
IDC Opening Keynote
Cybersecurity Under Pressure: Are We Ready for the Next Crisis?
IDC’s insights on escalating cyber threats, geopolitical impacts, regulatory pressures, and the strategic role of CISOs and IT leaders.
Bruno Durand
Event Sessions
One Day Event 10:20 am
Security, Resilience, and Continuity: Facing Increasingly Systemic Threats
Uriel Marie-Sainte
Avec une solide expérience en cybersécurité, Uriel a consacré sa carrière à aider les organisations à naviguer dans les complexités techniques des solutions de sécurité modernes. Aujourd’hui chez 1Password, il accompagne les clients et les partenaires dans le renforcement de la sécurité des accès et la résolution de défis tels que le fossé de confiance en matière d’accès et le shadow IT. Son expérience inclut des postes chez Zscaler, où il s’est concentré sur l’ingénierie des solutions et l’accompagnement des partenaires, faisant de lui une voix précieuse dans les conversations au carrefour de la sécurité, de la gestion des accès et de l’activation business.
Event Sessions
One Day Event 10:35 am
Your identity security architecture was built for humans. It’s time for a reset
A year ago, managing access for AI agents was a theoretical question. Today, NHIs aren’t at the gate — they’re inside the perimeter, acting autonomously and often invisibly.
This workshop will help attendees better understand how AI systems and agents are already interacting with their environments, what new risks are emerging with non-human identities, and how to apply governance principles suited to this new reality.
Amine Beyaoui
Thomas Gricar
Alexandre Lamy
Event Sessions
One Day Event 12:30 pm
Your number one IT vendor: the one you’ve never audited
Open source powers 90% of your applications, and it has become the number one target for attackers. What CISOs need to know about the risk they underestimate the most.
Guillaume Rameaux
Event Sessions
One Day Event 10:35 am
Your identity security architecture was built for humans. It’s time for a reset
A year ago, managing access for AI agents was a theoretical question. Today, NHIs aren’t at the gate — they’re inside the perimeter, acting autonomously and often invisibly.
This workshop will help attendees better understand how AI systems and agents are already interacting with their environments, what new risks are emerging with non-human identities, and how to apply governance principles suited to this new reality.
Partners
Sophos
Horizon3
Horizon3 is the AI-Native Proactive Security Company behind NodeZero®, the World’s Best AI Hacker™. NodeZero autonomously tests defenses at machine speed, safely uncovers and prioritizes exploitable attack paths, instantly verifies fixes, and drives a continuous hack, fix, verify loop that helps organizations shift the advantage from attackers to defenders.
1Password
ManageEngine