IT Security Summit Milan

11 May 2027 Milan, Italy
IT Security Summit Milan

IT Security Summit Milan

Securing the Enterprise in the Age of AI Agents

11 May 2027 Milan, Italy

Trust, Resilience, and Control in the Autonomous Enterprise

The IT Security Summit Italia 2027 brings together CISOs, regulatory authorities, and cybersecurity leaders from across the country to explore AI-powered defense, cyber resilience, OT security, sovereign AI, and post-quantum readiness.

With NIS2 reshaping compliance obligations for more than 100,000 Italian entities and growing geopolitical tensions intensifying the threat landscape, Italian boards of directors are under increasing pressure to treat cybersecurity as a strategic governance priority. According to IDC research, AI investments have become Italy’s top IT priority, narrowly ahead of cybersecurity, as the two agendas increasingly converge in practice.

According to IDC, European security spending is expected to grow to nearly $97 billion by 2028. However, more than 40% of European organizations experienced security budget cuts in 2025, while cyberattacks increased by 22% year over year, the highest rate globally. This tension between rising risks and constrained investments defines the challenge facing security leaders across Europe in 2027.

The summit offers strategic insights and peer-to-peer networking opportunities for Italian enterprises navigating NIS2, DORA, the EU AI Act, and the most complex threat landscape in the country’s digital history.

Why Attend?

From Strategy to Action: Cybersecurity Priorities

Gain strategic insight into the security challenges transforming European enterprises, from AI-powered threats and digital sovereignty requirements to OT resilience and quantum-era readiness. Take away practical frameworks, insights gained through peer-to-peer exchange, and a concrete roadmap to navigate one of Europe’s most demanding cybersecurity landscapes.

  • Govern AI agents while ensuring compliance with NIS2, DORA, and the EU AI Act.
  • Detect and counter AI-powered threats, synthetic identities, and deepfakes.
  • Strengthen OT security and critical infrastructure resilience across European operations.
  • Prepare for post-quantum cryptography and EU and UK quantum migration roadmaps.
  • Manage human, machine, API, and AI agent identities across hybrid environments.
  • Align cybersecurity investments with regulatory exposure, board accountability, and business resilience.

IDC Analysts

Roberta Bigliani

Roberta Bigliani

Group Vice President Global Lead for Industries

IDC

Read Bio

Massimiliano Claps

Massimiliano Claps

Research Director

IDC

Read Bio

Martina Longo

Martina Longo

Research Manager, CIO and CTO Buyer Insights

IDC

Read Bio

Andrea Siviero

Andrea Siviero

Vice President, AI-fueled Business Strategies

IDC

Read Bio

Joel Stradling

Joel Stradling

Senior Research Director, European Security

IDC

Read Bio

Speakers

Thomas Mascioli Colavecchi

Thomas Mascioli Colavecchi

Chief Information Security Officer

Polo Strategico Nazionale

Read Bio

Giovanni Zanetti

Giovanni Zanetti

Cybersecurity Operations Manager e Vicepresidente AIPSI

Fondazione Milano Cortina 2026

Read Bio

Stefano Righetti

Stefano Righetti

Head of IT Governance, Information Security & Strategy

Acciaierie d'Italia

Read Bio

Luca Della Giovanna

Luca Della Giovanna

Chief Information Security Officer

Humanitas

Read Bio

Our Partners

Key Topics

Securing AI in a Regulated Continent

Exploring how European enterprises can govern AI agents and autonomous systems within the constraints of NIS2, DORA, and the EU AI Act, while maintaining operational trust, accountability, and compliance across increasingly AI-driven environments

Europe’s Cyber Arms Race

Examining how AI is intensifying both cybercrime and cyber defense across Europe, as adversaries exploit synthetic identities and deepfake technology while European SOC teams race to deploy AI-powered detection, response, and dynamic playbook generation.

Identity and Access in the Post-Perimeter Enterprise

Exploring how identity has become the critical control layer for European enterprises navigating hybrid cloud, NIS2 access governance requirements, and the explosive growth of non-human identities including AI agents and machine-to-machine access.

Securing the European Digital Supply Chain

Supply chain attacks have become one of the most significant cybersecurity vectors in Europe. This theme explores how European organizations are strengthening software assurance, third-party risk management under NIS2, and AI bill-of-materials practices as 65% of European agentic AI deployments move toward BOM requirements by 2027.

Cyber Risk, Boards, and the Compliance Imperative

European boards face unprecedented accountability as NIS2 and DORA impose direct executive liability for cyber-risk management. This theme examines how European leaders and boards are quantifying risk, aligning security investment with financial exposure, and navigating the most demanding regulatory environment globally.

Sovereignty, Regulation, and Digital Trust

Analyzing how the EU AI Act, data residency mandates, NIS2, DORA, and sovereign cloud requirements are reshaping enterprise architecture and governance across Europe. With 40% of European governments expected to mandate sovereign AI by 2028, the stakes for strategic planning have never been higher.

2027 Prediction

By 2028, 25% of European enterprises will use autonomous agent-powered cyber-risk quantification platforms to turn security metrics into financial exposure, guiding budgets, controls, and M&A risk assessments

Venue

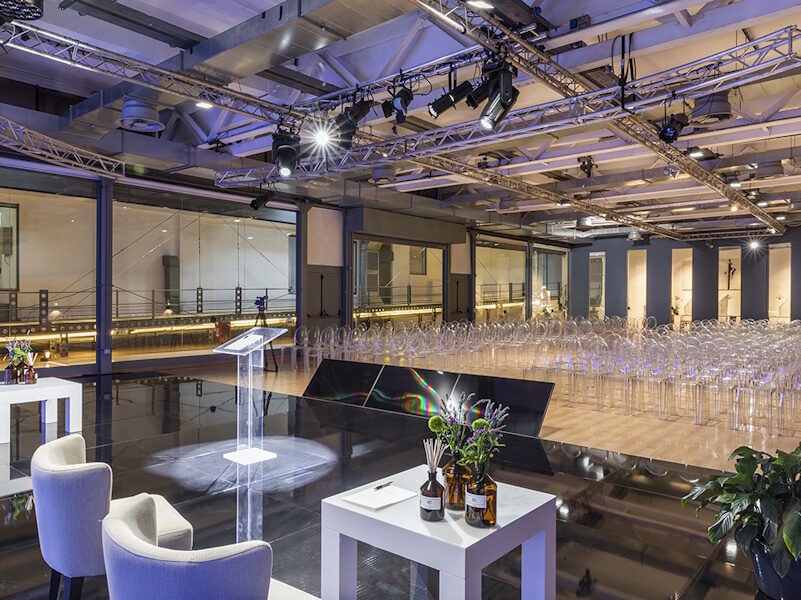
Magna Pars Event Space

Via Tortona 15, 20144, Milan – Italy


How to Attend

Attendance is free of charge, subject to completion of the registration form, for professionals working in the following sectors: Manufacturing, Automotive, Fashion, Finance, Banking and Insurance, Retail, Energy and Utilities, Media, Government, Healthcare, Education, Transport, Logistics, Telecommunications, and Personal and Professional Services.

The event will take place on May 11, 2027, starting at 9:00 AM.

Access is restricted to eligible industry professionals. Registration is not open to non-sponsoring ICT companies (vendors, distributors, resellers, VARs, and system integrators), ICT consulting and services firms, private individuals, or freelancers.

The official language of the event is Italian.

Knowledge Hub

The NIS 2 directive – where are we now?

The deadline for the transposition of the EU’s second Network and Information Systems Security directive (NIS 2) came and went in October 2024 with only a handful of member states having completed the task.

Read more

European ICT spending implications of NATO’s 5% GDP spending target

At the 2025 NATO Summit in The Hague a few weeks ago, member states pledged to allocate 5% of their annual GDP to core defense requirements and defense- and security-related expenditures by 2035.

Read more

IAM 2025: The Rise of the Machines

Identity and access management (IAM), and by extension, identity security, is one of the most pervasive and impactful challenges facing all European organizations today, from an operational and risk management perspective.

Read more

Not the right event for you?

Don’t worry! We organize a variety of events designed to inspire original ideas, share the latest industry insights, and connect professionals like you. Simply sign up for event invitations, and we’ll notify you whenever a new event matches your interests.

Sign up